This is a writeup & guide to the hardware hacking challenge I made, Keep talking and everybody explodes, from the finals phase of OmniCTF 2026.
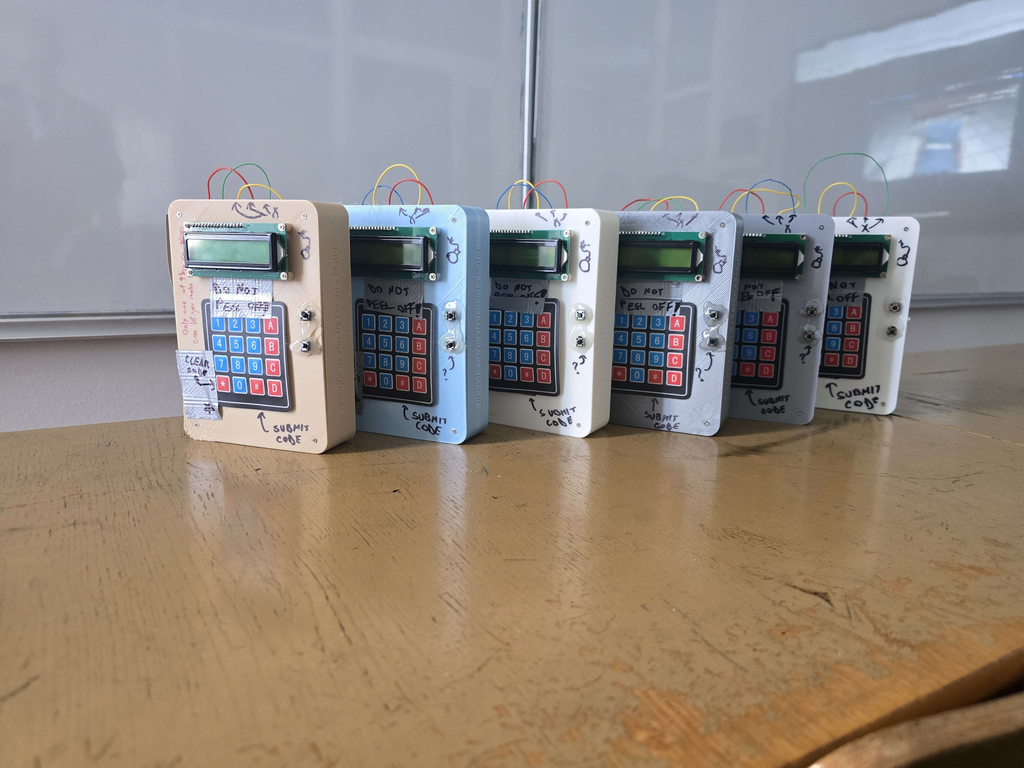
It was pretty fun to create it. It was a challenge by itself to make 14 identical boxes people could solve.
The guide and everything else you need to make the hardware chall at home is here: https://github.com/fersetamatei/OmniCTF-hardware
The challenge has 3 flags located in different places: 1 on the EEPROM chip of the Arduino and 2 on the Flash chip.
Flag 1 – defuse the bomb (intended solve)
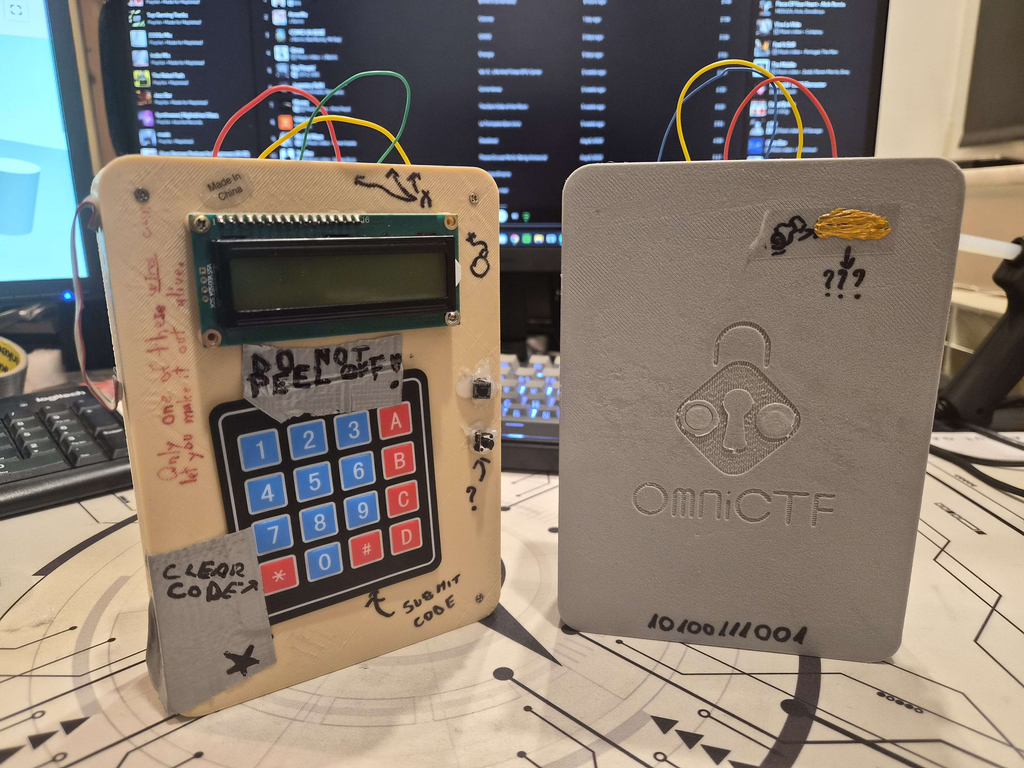
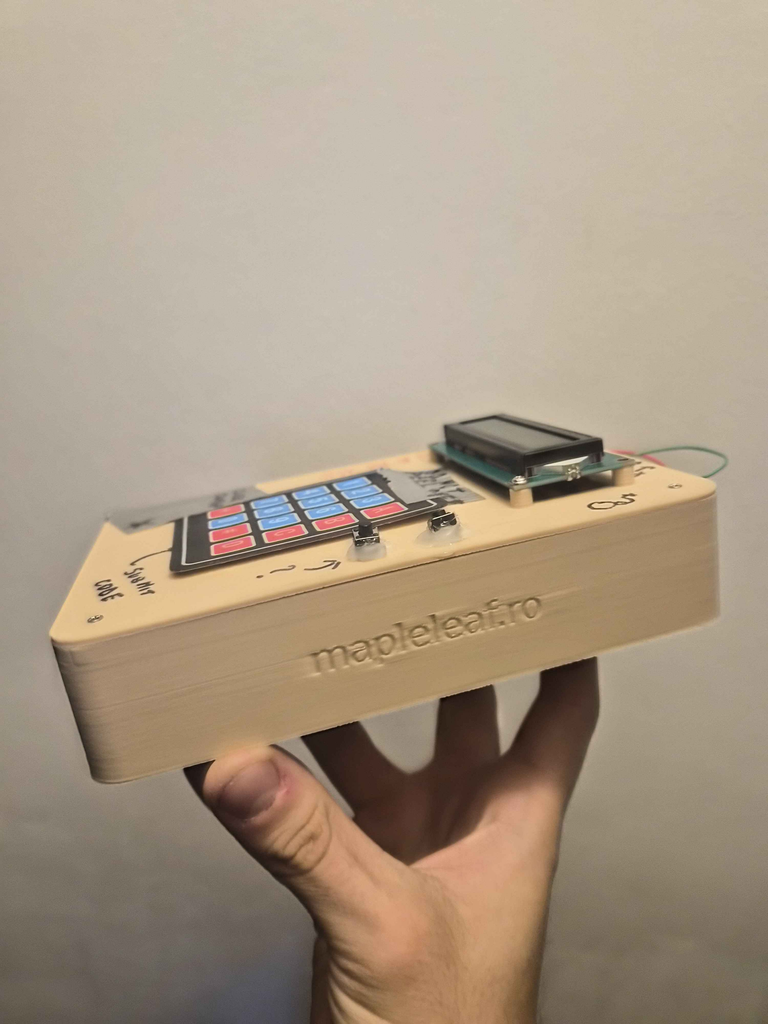
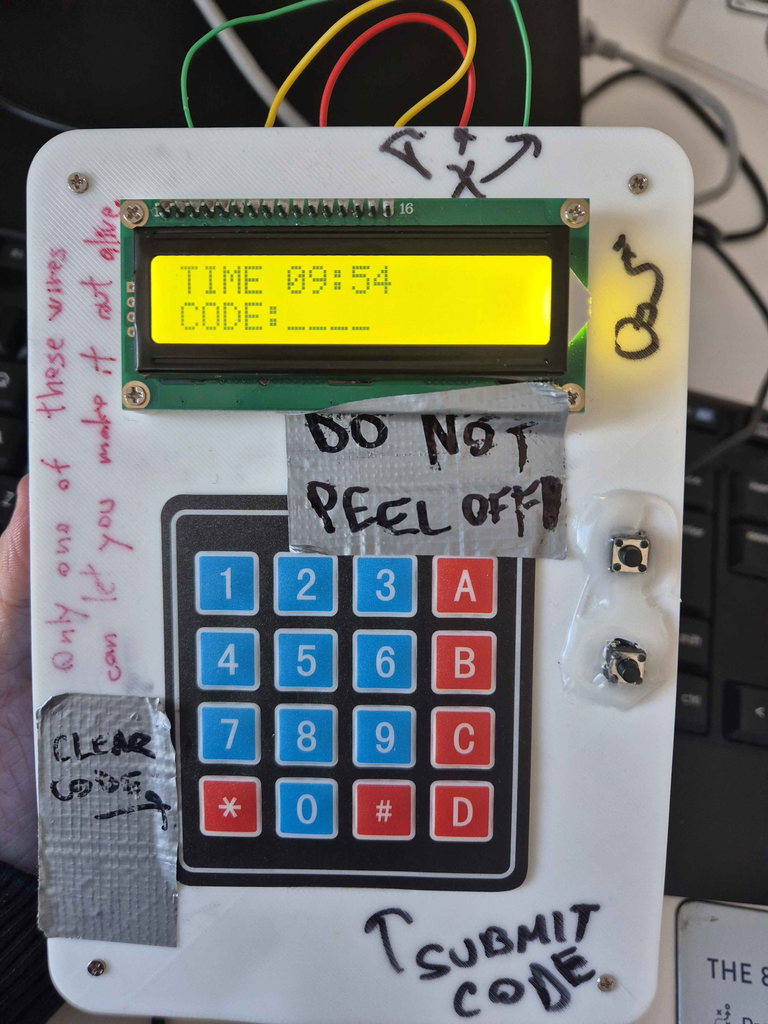
On the bomb there were a bunch of random messages, wires, easter eggs and other stuff.
Step by step instructions to defuse the bomb:
- Cut the red wire to be able to input the right bomb code.
- Extract the bomb code from the flash firmware (dump through USB). The code can be found in plaintext there.
- Input the code after cutting the red wire. You get the first flag after that.
Flag 2 – EEPROM
Flag 2 is stored in plaintext in the EEPROM. There are some EEPROM dump scripts online, you can use any to dump the EEPROM and read the flag. Here is what I used: https://github.com/Reefwing-Software/Arduino-EEPROM-Hex-Dump (only works if you reflash the Arduino, hence why there were unlimited resets after getting the first flag).
Flag 3 – easter egg codes
Flag 3 can be found by inputting the 5 easter egg codes that can be found around the bomb:
1057– found under the keypad1337– found in binary behind the bomb6767– the hint for this code is shown when pressing the random message button0001– hinted by the “Brute Force?” message0777– under the scratch-off sticker on the back
Upon inputting the 5 easter egg codes you get the flag.
– 12th-grade student at Colegiul Național de Informatică “Tudor Vianu”
– President of Vianu Cybersecurity Club
– Trainer at Atlantykron
– Volunteer at Astrofest, Hallo Fest, Sci-Fi Fest, Poli Fest
– Pseudo-Owner of Bacon, my cat.
More about me here.